

Bancwr
Keep your brand's identity under your control, on a server you run.
Bancwr lets your team post as one Nostr identity without handing it to anyone. It runs on your own server, so no vendor, Diogel included, holds it. You decide who can act for the brand, and every signature is logged.
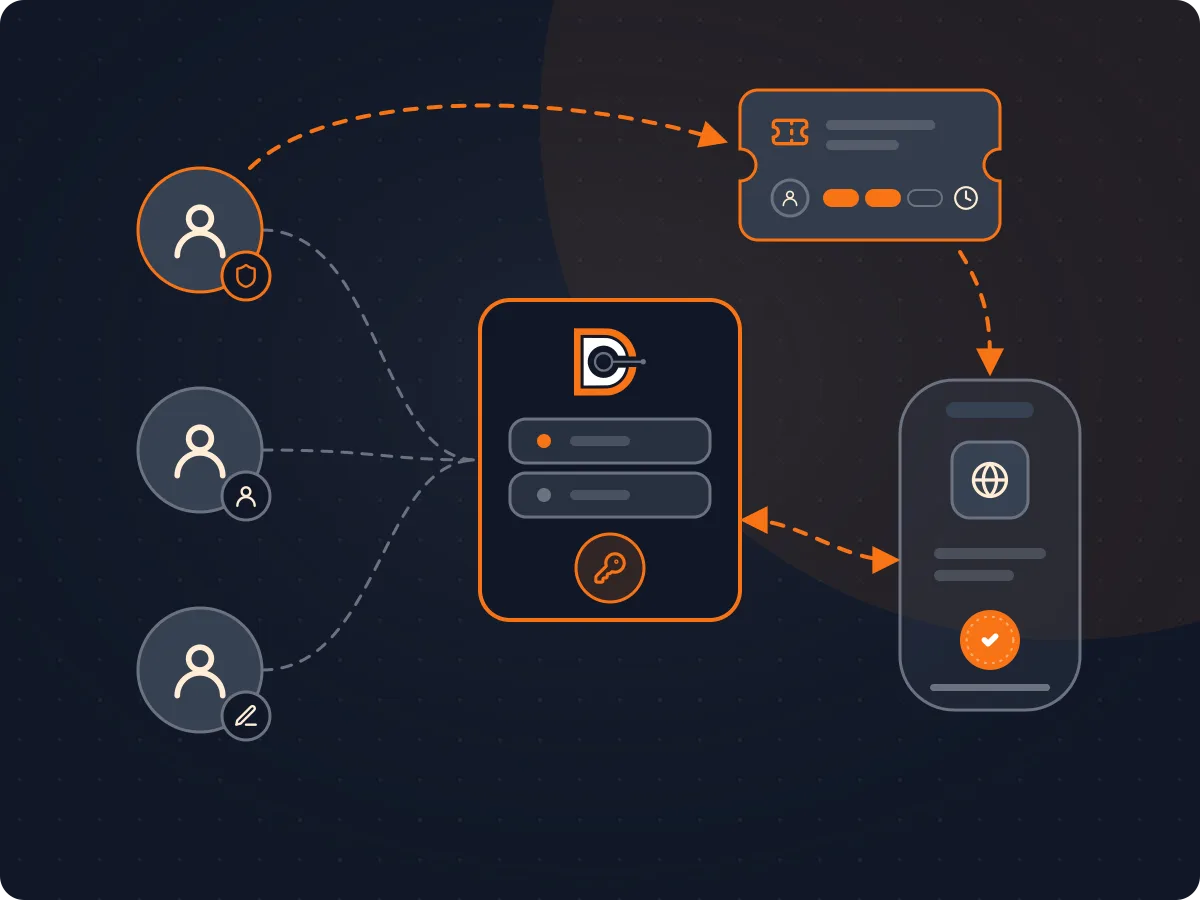
Shared signing authority, no shared key
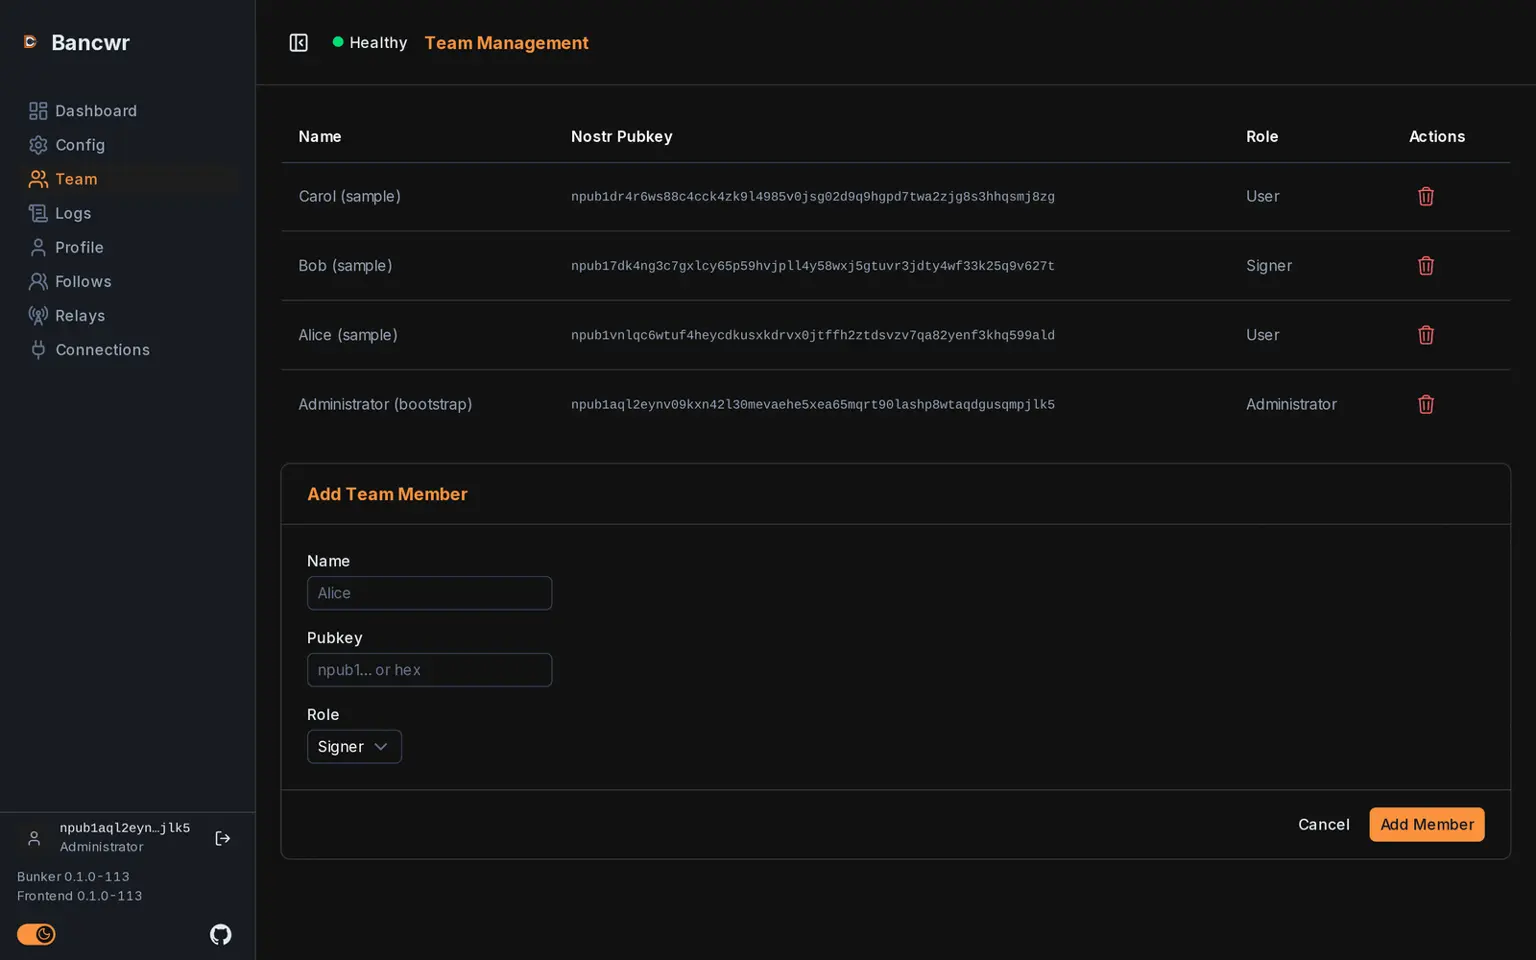
One Nostr identity, many members. Bancwr keeps the nsec on your server and your team works through it. Members sign in to the web console with a NIP-07 extension or a NIP-46 bunker:// string, and Bancwr never asks anyone for a private key.
- Brand accountsOne Nostr identity, multiple registered members
- Three rolesAdministrator, user, and signer, checked on every request
- No key distributionMembers never receive the nsec, and there is no field to enter one
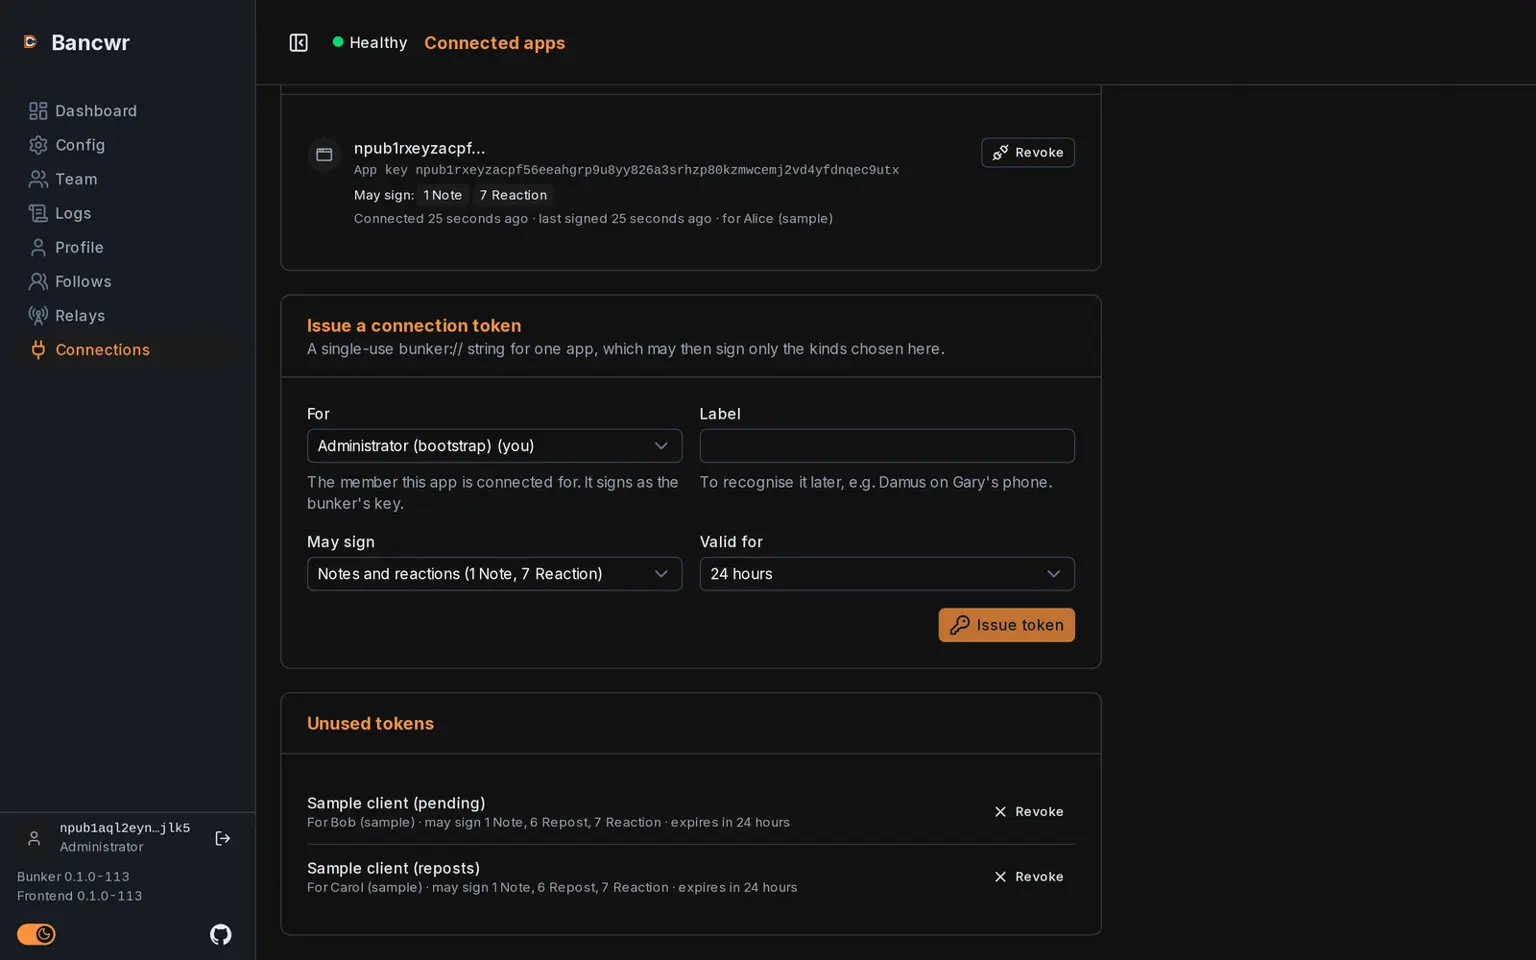
Controlled app connections over NIP-46
Nostr apps use Bancwr as a remote signer, but only once an administrator lets them. Each connection starts from a single-use token issued for a named member and limited to the event kinds you list. There is no "sign everything" grant.
- Kind-scoped tokensSingle-use, limited to listed event kinds, valid for 1 hour to 7 days
- Revocable connectionsRevoke any connection, and removing a member ends theirs
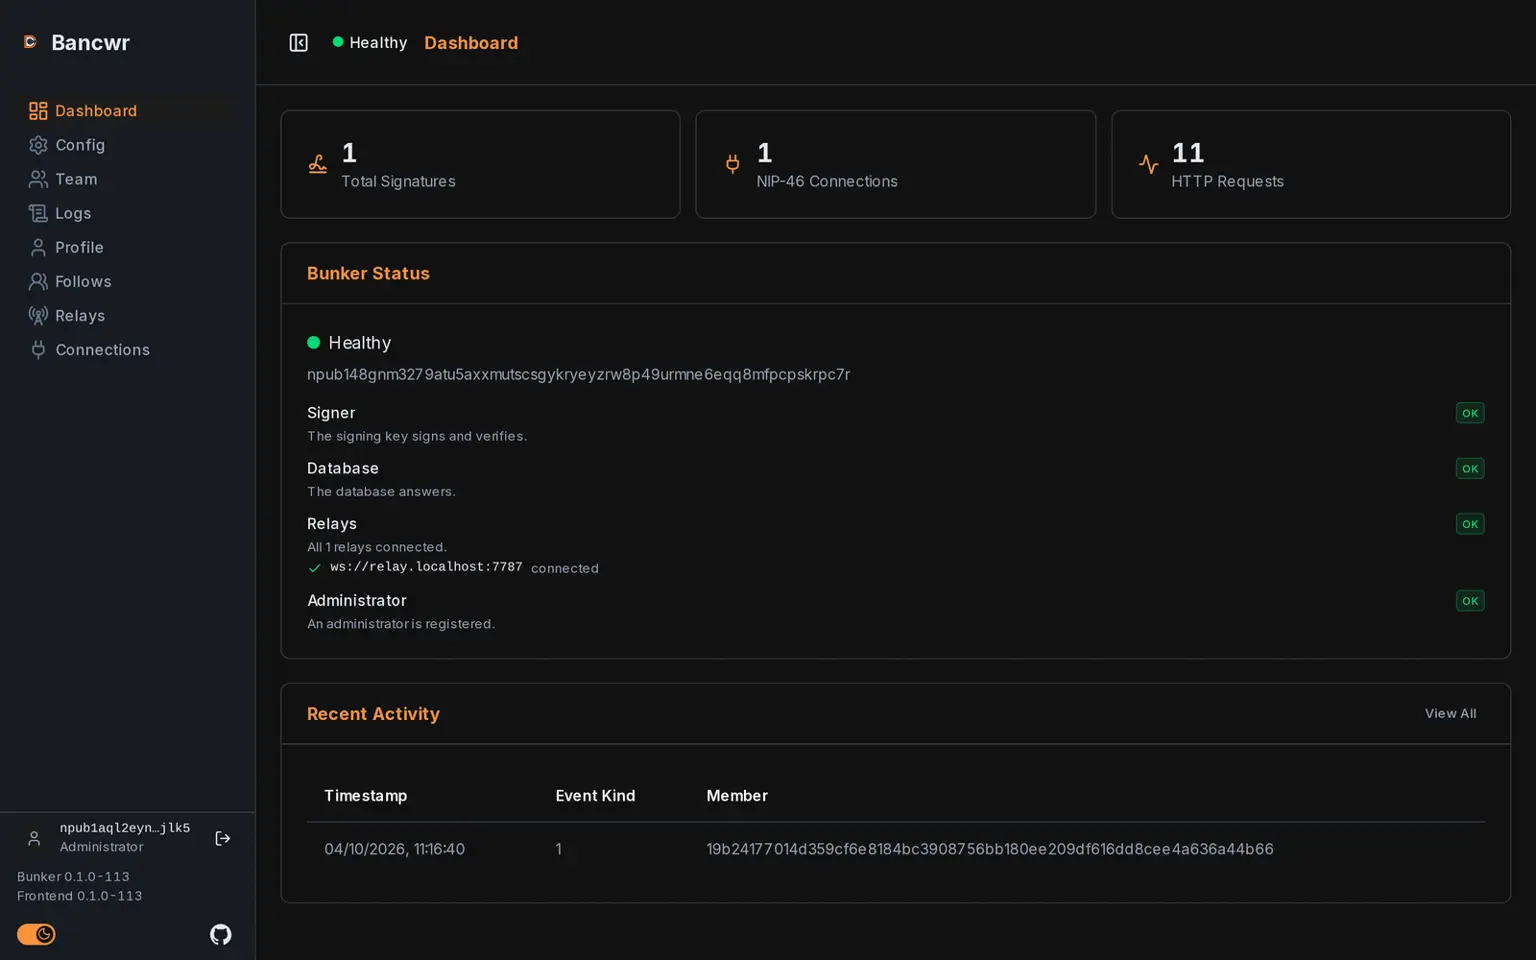
- Signing logAdministrators see recent signatures by event, kind, member, and time
Your server, your key
Run Bancwr with Podman or Docker Compose from versioned images on GitHub Container Registry. Signing happens over NIP-46 only. The HTTP API behind the web console manages the bunker and never signs.
- Podman or DockerCompose file and published images for the bunker and console
- Locked-down by defaultDistroless, non-root containers, and a console reachable only behind your TLS proxy
- No open signing portThe bunker API only accepts requests the console has signed
At a glance
What Bancwr brings to organisational Nostr signing.
Self-hosted bunker
The nsec stays on infrastructure you run
NIP-46 remote signer
Works with Nostr apps that support bunker:// connections
Roles
Administrator, user, and signer access to one identity
Kind-scoped connections
Each app signs only the event kinds you allow
Revocation
Cut off an app or a member without rotating the key
Signing log
See what was signed recently, by whom, and when
Take control of your team's Nostr identity
Self-host Bancwr and decide who can sign on behalf of your organisation.